Vulnerability Management Process Flow Chart
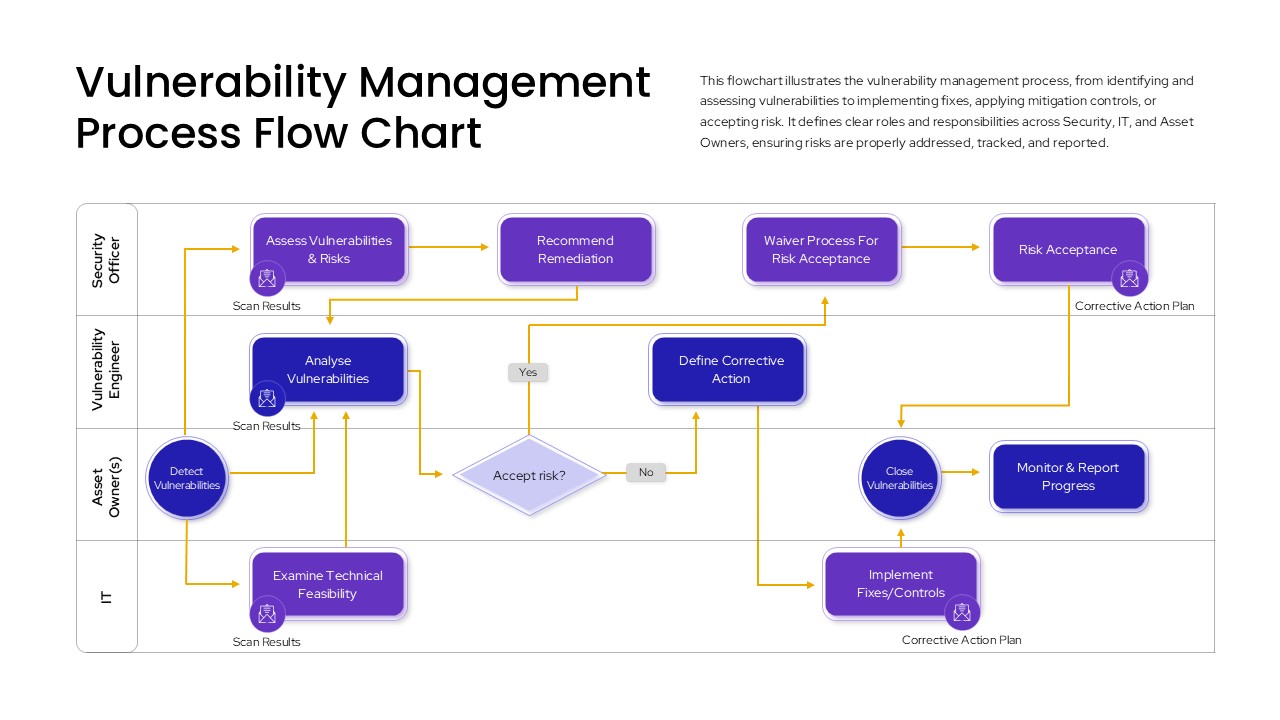


The Vulnerability Management Process Flow Chart provides a clear visual framework for managing security weaknesses from initial detection through remediation and ongoing monitoring. It shows how security teams can identify vulnerabilities, review scan results, assess potential risks, and determine the appropriate response. The swimlane structure separates responsibilities between the Security Officer, Vulnerability Engineer, Asset Owner, and IT team, helping organizations understand who is involved at each stage of the process.
The workflow begins with detecting vulnerabilities and analyzing the findings to understand their severity and potential impact. The team then examines technical feasibility and recommends suitable remediation actions. A risk decision point determines whether the identified risk should be accepted or addressed through corrective measures. If the risk is accepted, it moves through the formal risk acceptance process. If action is required, the responsible teams define corrective measures and implement fixes or security controls.
The Vulnerability Management Process Flow Chart presents a structured workflow for identifying, assessing, prioritizing, and resolving security vulnerabilities across an organization. The process begins with detecting vulnerabilities and analyzing scan results, followed by technical feasibility checks and remediation recommendations. Teams can then decide whether to accept the risk or define corrective actions. Accepted risks move through the risk acceptance process, while identified issues proceed to fixes and security controls. The swimlane structure clearly separates responsibilities across Security Officers, Vulnerability Engineers, Asset Owners, and IT teams, making it easier to understand ownership at each stage. This flow chart can be used to explain vulnerability assessment procedures, remediation workflows, risk decisions, corrective action plans, and ongoing security monitoring in cybersecurity presentations, security reviews, IT meetings, and compliance discussions.
Key Process Stages
- Detect Vulnerabilities: Identify security weaknesses through scans and assessments.
- Analyze Vulnerabilities: Review findings and determine their potential impact.
- Recommend Remediation: Propose suitable actions based on risk and technical findings.
- Accept or Address Risk: Decide whether to accept the risk or proceed with corrective action.
- Define Corrective Action: Establish the required steps, owners, and remediation plan.
- Implement Fixes or Controls: Apply patches, configuration changes, or other security measures.
- Monitor and Report Progress: Track remediation status and communicate security progress.
Frequently Asked Questions
How can security teams use this vulnerability management template?
What makes this vulnerability management flow chart effective for presentations?
Login to download this file

Item ID
SB05722Designed By
Naseeba Sithara


Related Templates

Resilience & Vulnerability Comparison Template for PowerPoint & Google Slides
Comparison
Business Process Management Flow Diagram Template for PowerPoint & Google Slides
Process
Incident Management Flow Process template for PowerPoint & Google Slides
Flow Charts
Consent Management System Process Flow Template for PowerPoint & Google Slides
Process
Wastewater Treatment Process Flow Chart Template for PowerPoint & Google Slides
Flow Charts
Animated Process Flow Chart PowerPoint template
Infographics
Flow Chart template for PowerPoint & Google Slides
Flow Charts
Eight Box Flow Chart Diagram Template for PowerPoint
Flow Charts
UX Flow Chart PowerPoint Template
Process
Flow Chart Template For PowerPoint Presentations
Flow Charts
Flow Chart Diagram Template for PowerPoint & Google Slides
Flow Charts
Flow Chart Diagram template for PowerPoint & Google Slides
Flow Charts
Flow Chart Infographics Template
Flow Charts
Flow Chart Template for PowerPoint & Google Slides
Flow Charts
Flow Chart Presentation Template
Flow Charts
Flow Chart Infographics for PowerPoint & Google Slides
Flow Charts
Flow Chart template for PowerPoint & Google Slides
Flow Charts
Free Flow Chart Template
Flow Charts
Free
Cross Functional Flow Chart PowerPoint Template
Flow Charts
Attribution Modeling Flow Chart Template for PowerPoint & Google Slides
Flow Charts